João Mota
CTO | CMO
The indirect obligations of the supply chain
When talking about the NIS2 Directive, the first question usually is: “Is my company covered?”
It is a relevant question, but perhaps it is no longer the most important one for your company.
In the coming years, many small and medium-sized businesses will feel the impact of NIS2 without ever receiving a notification from a regulatory body. The reason is simple: their customers will start demanding more cybersecurity guarantees from all the suppliers they work with.
That is, even if your company does not have direct obligations under the Directive, you may have to demonstrate that you adequately protect the information, systems, and processes to continue to be part of the supply chain.
Trust has become part of the business
NIS2 came to reinforce the responsibility of organizations considered essential and important in risk management. However, this responsibility does not end within their premises.
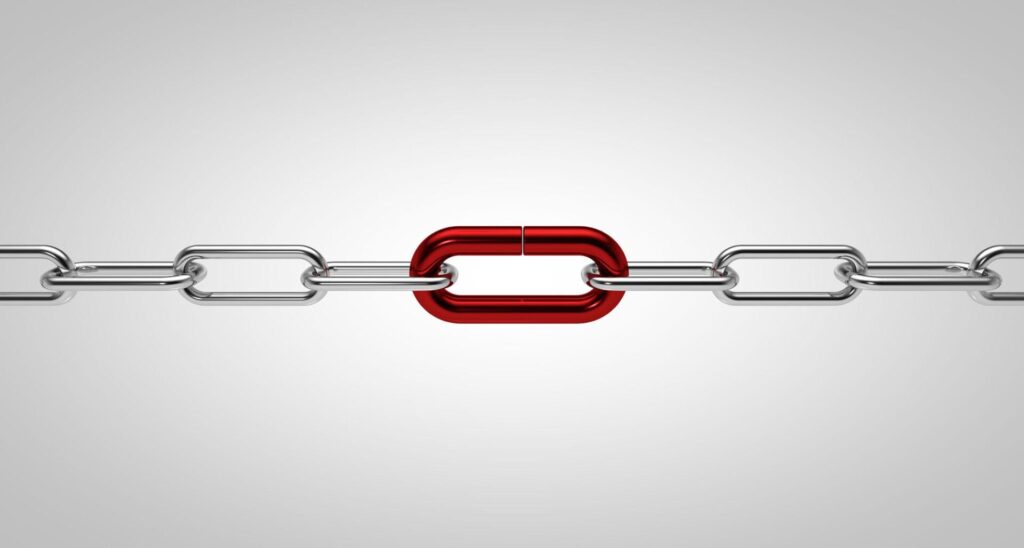
Companies are also required to assess the risks associated with the partners, suppliers, and service providers with whom they work daily. After all, it is enough for one link in the chain to be vulnerable for the entire organization to become exposed.
This reality is changing the way many companies choose their suppliers. In addition to quality, price or responsiveness, a new factor is starting to gain importance: the maturity of the company in terms of cybersecurity.
That is why requests for information about security policies, backup systems, multi-factor authentication, infrastructure monitoring, or incident response plans are starting to emerge. Not because all of these companies are required to comply with NIS2, but because their customers need to reduce the risk associated with their supply chain.
The impact could reach any sector
It is easy to think that this topic only concerns large organizations, but the reality is quite different.
An agricultural company that supplies an food industry, a manufacturer that works for a multinational company, a transport company, a service provider or a technology consultant may, at any time, be called upon to demonstrate that they adopt good cybersecurity practices.
In most cases, no one will ask them whether they comply with NIS2. What will be evaluated is whether they represent a risk to the customer’s business or not.
And that difference is important.
Increasingly, cybersecurity is no longer seen solely as a technical obligation but has become a factor of business trust. A prepared company conveys greater credibility, responds more quickly to customer requests, and positions itself more competitively when participating in new projects or tenders.
Waiting for the first order may be too late
Many organizations only start to become concerned about these issues when they receive a questionnaire from a customer or an unexpected requirement in a hiring process.
At that time, time is reduced and the necessary adjustments may prove more complex than expected. Defining policies, reviewing processes, implementing protective measures, or fixing vulnerabilities are tasks that require planning and cannot be solved overnight.
Preparing the company in advance allows it to respond more confidently to market demands and to transform cybersecurity into a differentiating factor, rather than a hasty response to a new obligation.
As has happened with quality, data protection or sustainability, information security is becoming a criterion of trust among companies.
The question, therefore, may no longer be “Is my company required to comply with NIS2?”
The real issue is quite different:
“If a customer asks me for evidence of my cybersecurity practices today, will I be prepared to answer?”
It is this response that could make the difference between continuing to be part of the supply chain or seeing a business opportunity pass to another supplier.
👉 Want to know if your company is prepared to meet the demands of customers and the supply chain? Schedule a conversation with João Mota by https://calendly.com/joaomotaquantinfor/30min and discover how Quantinfor can help you strengthen your cybersecurity posture.
